
You've been asked to add an SPF record, or you've found spf=softfail in a message's headers. SPF (Sender Policy Framework) is a TXT record in your DNS that lists the servers allowed to send email with your domain in the bounce address. The mail provider that receives a message, such as Gmail or Outlook, checks the sending server against that list.
A softfail usually means a message came from a server that isn't on the list, and the record ends in ~all. If you're here because of spf=softfail, jump to what softfail means. If you're here to publish a record, jump to setting up SPF.
How SPF, DKIM and DMARC fit together
SPF is one of three checks, and each one checks one thing. SPF checks the server that sent the message against the list for the domain in the bounce address. DKIM checks a signature that the sender adds to each message. DMARC checks whether SPF or DKIM passed for the domain in the From address, which is the address people read.
The service that sends a message sets its bounce address, so that address can be at the service's domain and not yours. That is why a message can pass SPF and still fail DMARC. SPF passed for the service's domain, and DMARC counts a pass only for the domain in your From address.
DKIM works the same way. A service can sign with its domain and not yours. A signature counts for DMARC only when the domain that signed it matches your From address. So for DMARC, SPF or DKIM has to pass for your domain. A softfail isn't a pass, so DMARC never counts it.
How a mail provider checks SPF
The bounce address is where failure notices go. You can see it in a delivered message's headers as Return-Path, and as smtp.mailfrom= in the Authentication-Results line. SPF checks that address, and it does not look at the From line.
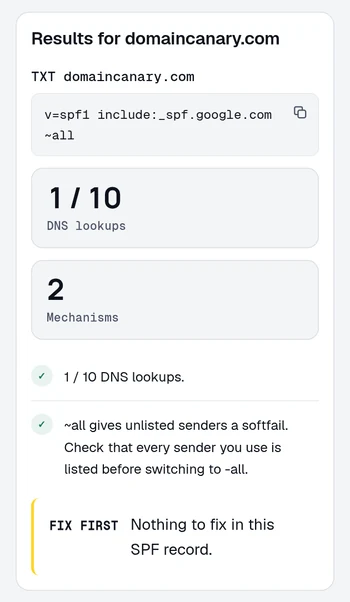
The receiving mail provider takes the domain from the bounce address and looks up its SPF record. This is the record we publish for domaincanary.com:
Every SPF record starts with v=spf1. The next part, include:_spf.google.com, adds the servers on Google's list. With ~all at the end, we're telling mail providers that any other server probably isn't allowed to send for us.
The mail provider reads the record from left to right and compares each part with the server that sent the message. The first part that matches sets the result. In our record, a server on Google's list gets pass. Any other server reaches ~all, which gives softfail.
A pass means the server is on the list of the domain in the bounce address. When that domain belongs to a sending service, the pass is for the service's list, and your record wasn't checked.
To pass DMARC with that service, set up DKIM for your domain there. If it offers a custom bounce domain, also called a custom return-path, set that up as well, so your domain is in the bounce address.
SPF results
A part of the record can have a mark in front of it, which is +, -, ~ or ?.
| Result | What causes it |
|---|---|
pass | The first part that matches the server has +, or doesn't have a mark. |
fail | The first part that matches has -. |
softfail | The first part that matches has ~. |
neutral | The first part that matches has ?, or nothing matches and the record doesn't have an ending. |
none | The domain doesn't have an SPF record. |
temperror | A temporary error, usually a DNS lookup that failed. |
permerror | The record can't be read, the domain has two SPF records, or the mail provider stops after 10 lookups without reaching the server. |
The ending is the last part of a record, such as ~all or -all. The mark is usually on the ending, which is why people link softfail to ~all. But a mark can sit on any part. Our tools and our SPF syntax reference call a part a term.
What spf=softfail means
spf=softfail is the result of an SPF check. It usually means the server that sent the message isn't on the list in a domain's SPF record, and the record ends in ~all. The record that gets checked belongs to the domain in the bounce address, which the sending service sets.
Whose server softfailed
The fix depends on whose record was checked and whether the server is yours. This is an example header line with example domains:
- Find the domain in the address after
smtp.mailfrom=. The mail provider checked that domain's record. - Find the IP address of the server that sent the message. In the example it is
192.0.2.1, in the parentheses afterspf=softfail. - Look the IP address up, and see whether it belongs to a service you send email from.
Some mail providers leave the IP address out of that line. Then paste the headers into our free email header analyzer, which lists each server that handled the message with its IP address. In a DMARC report, it is the source IP.
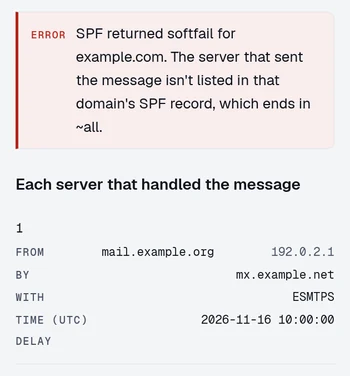
If the domain after smtp.mailfrom= isn't yours, it belongs to a sending service or a forwarder. The mail provider didn't read your record, so changing it won't help. For a service you use, set up DKIM for your domain at that service, so the message can pass DMARC.
If the domain is yours, the mail provider read your record and the server didn't match. When the server isn't yours, leave the record alone, because softfail is the right result. When it is yours and isn't in the record, add it under adding a sender.
When the server is yours and you expect the record to cover it, the record may have changed a short time ago. A mail provider can still hold the old one, so test again later. Or the part that should match doesn't cover this server, such as an ip4 part with a wrong address.
If the domain is a subdomain of yours, such as billing.example.com, the mail provider read the record at that exact name, and not the one at example.com. Add the server to the subdomain's record.
Forwarded mail
A forwarded message can softfail when your record is correct. The forwarder's server sends the message on, and it isn't in your record. If the forwarder kept your bounce address, the next mail provider checks your record and gives softfail.
Leave the record alone, and don't add the forwarder's server to it. That would let any message from that server pass SPF for your domain. A forwarded message can still pass DMARC with its DKIM signature, as long as the forwarder didn't change it.
What mail providers do with a softfail
Under the SPF standard, RFC 7208, mail providers should not refuse a message for a softfail alone, but they may look at it more closely. What happens to a message is up to the mail provider that receives it.
For DMARC, the check on the From address, a softfail is a failure. Under the DMARC standard, RFC 9989, DMARC counts SPF only when SPF passes. The message can still pass DMARC with a DKIM signature from the domain in the From address. Our DMARC alignment guide covers how closely the domains have to match.
Adding a sender
A service that sends email for you goes into the record you already have. Don't publish a second SPF record, because two SPF records give permerror. This is our record with a placeholder for a second service:
The Google include is ours. Replace PLATFORM_INCLUDE with the domain from the service's documentation, so the part reads include: and then that domain.
Then count the DNS lookups. Each include, a, mx, ptr, exists and redirect part counts as one, and so do the parts inside an include. A mail provider stops after 10 lookups. A sender it hasn't reached by then gets permerror, and senders it has reached still pass. The all, ip4 and ip6 parts don't count toward the 10-lookup limit.
Our free SPF checker follows every include and counts the lookups against 10. Before you publish a changed record, paste it into our SPF change pre-flight, which shows the count. Our SPF lookup limit guide covers getting back under 10.
When to change ~all to -all
We recommend starting with ~all, and Google's example record ends the same way. Microsoft recommends -all, and its example record ends in -all.
With -all, a server that isn't on the list gets fail, and under the SPF standard mail providers may refuse the message. That goes for forged mail and for mail from a service you forgot.
You don't have to change, because for DMARC a softfail and a fail are both SPF failures. If you do change, wait until every service that sends for you is in the record and signs with DKIM for your domain.
Don't end a record in +all or ?all. With +all, any server on the internet passes SPF for your domain. With ?all, you aren't telling mail providers whether other servers are allowed.
Setting up SPF
- List every service that sends email for your domain, such as staff email, the invoice app, the marketing tool and the website's contact form.
- Get the include for each one from that service's documentation. Our provider pages quote each service's include and say where it goes.
- Write one record that starts with
v=spf1, has each include, and ends in~all. If your domain already has an SPF record, add to that record and keep its parts. - For a server that you run, add
ip4:followed by the server's IP address, before the ending. - Paste the record into our SPF change pre-flight and confirm it needs 10 lookups or fewer.
- Publish it as a TXT record at your domain, in place of the old SPF record if there is one. Google says SPF can take up to 48 hours to start working.
- Send a test message from each service to a mailbox outside your company.
- In each test message, find
spf=passin theAuthentication-Resultsline. - Check which domain follows
smtp.mailfrom=in the same line.
If that domain is the service's and not yours, DMARC doesn't count the pass, and the fix is under how a mail provider checks SPF. If a test shows softfail, follow whose server softfailed.
Keeping the record up to date
The record goes out of date when someone at your company starts sending through another service. DMARC reports show it. Mail providers send them once you publish a DMARC record that asks for them.
We read those reports for you. Your first domain is free, and we send you a digest every Monday. When your SPF record changes, the digest shows it. On a paid plan we email you as soon as we find out that a sender has started failing DMARC.
Count your SPF record's lookups
Every include followed, the total against the limit of ten, and the senders in the record.
Free · No signup · The result names what to change
Questions
Is SPF softfail a fail for DMARC?
Yes. DMARC counts SPF only when SPF passes. The message still passes DMARC if it has a DKIM signature from the domain in your From address. If it doesn't, DMARC fails and mail providers apply your DMARC policy.
Why does my own mail get spf=softfail when I forward it?
The forwarder's server sent it on, and that server isn't in your record. Leave the record alone. The forwarded message can still pass DMARC with its DKIM signature.
Does SPF stop email spoofing?
No, you need DMARC as well. SPF checks the bounce address, and people don't see that address. Someone can pass SPF for a domain they control and still put your address in the From line. DMARC is the check on the From address.
How long does SPF take to work?
Mail providers look the record up each time they check a message. So a change applies once their saved copy of the old record expires. Google says that can take up to 48 hours.
What do Gmail and Yahoo ask senders for?
Gmail asks every sender for SPF or DKIM. From anyone who sends 5,000 or more messages a day to Gmail, it asks for SPF, DKIM and a DMARC record. Yahoo asks bulk senders for the same three.
Keep reading
Checking as you go? The DMARC checker reads the policy you are moving up, the SPF and DKIM checkers show whether your senders will survive it, and the report analyzer reads an aggregate report you already have. No signup.
DomainCanary is a DMARC enforcement service that protects your domain from email spoofing without blocking your own mail.